Showing posts with label project risk management. Show all posts

Friday, April 26, 2013

Risk Management Foundation


In this chapter, we are going to cover the foundational concepts of Risk Management.

Let us start with the official definition of the term “Risk” - A Risk is an uncertain event or condition that, if it occurs, has a positive or negative effect on a project’s objectives. The term uncertain means we are not sure whether the event will happen. There is a likelihood that the event will happen and if it does, there will be consequences.

The practice standard for risk management says that – Dealing with threats and opportunities together typically leads to a gain of synergies and efficiencies.

While handling project risks we typically use two terms:
Individual Risk – A risk that may have an impact on project objectives
Overall Risk – Reflects the overall uncertainty of the project as a whole

During the course of the chapters on the PMI RMP Exam series, I have said this numerous times and since the concept is so important, I don’t mind saying it again. Risk Management is an iterative activity and must start at the early stages of a Project Lifecycle.

Who is Responsible for Risk Management?

This is a million dollar question which you already know the answer, don’t you?
Everyone

Yes, everyone in the project including all the stakeholders are responsible collectively to manage the risks in the project. But, the key people who drive the risk management effort for the whole project are the Risk Manager and the Project Manager. It would be a god idea to have a Risk Manager for every project but, in most cases there is no dedicated risk manager for a team and the Project Manager doubles over as the risk manager as well.

Common Risk Management Mistakes

As said in the previous section, without a collective effort from everyone in the team, risk management could fail very easily. But, this isn’t the only problem in most projects. Some of the common mistakes that people do in projects are:
• Conducting no risk management activities at all
• Even if risk management activities are conducted, it is done by one or a select few people only
Responsibilities of the Project Manager & Risk Manager with respect to Project Risk Management:
The following are some of the responsibilities of the Project Manager and Risk Manager:
• Getting the senior management’s support and carrying out as well as encouraging strong communication
• Determining risk tolerance levels & tailoring the risk management activities in the project to suit the needs of the project as well as the risk tolerance levels
• Generating an approved Risk Management plan that reflects the project’s risk management processes
• Carrying out and overseeing the Risk Management Plan activities and processes
• Reporting as required
• During project closure – determining what went well and where there are areas for improvement.
• You document lessons learned so that future projects could use them

Remember, just earlier on in this chapter I said that risk management is everyone’s responsibility but according to the practice standard for risk management though risk management is everyone’s responsibility, the project manager will be held accountable for successful completion of risk management activities in the project.

Prev: Introduction to Practice Standard for Risk Management

Next: The Risk Management Processes

Friday, June 15, 2012

Section Summary – The Risk Management Plan


In the previous few chapters, we took a detailed look at the Risk Management Plan. Let us now quickly summarize what we have learnt so far about the RM Plan…

• The RM Plan is the heart and soul of Risk Management
• The purpose of the Risk Management Plan is to define how risks will be managed, monitored and controlled throughout the project
• The RM Plan is created during the Plan Risk Management process of the PMBOK guide.
• The following are the inputs used in creating the RM Plan:
o Project Scope Statement
o Cost Management Plan
o Schedule Management Plan
o Communications Management Plan
o Enterprise Environmental Factors &
o Organizational Process Assets
• The Risk Management Plan is created using a Planning Meeting
• The Planning meeting is critical to the project’s success because they create the foundation and the roadmap for all risk related activities in the project
• As per the PMBOK guide, the RM Plan contains 10 sections. They are:
o Risk Methodology
o Roles & Responsibilities
o Budgeting Information
o Timing Information
o Risk Categories
o Definition of Risk Probability & Impact
o The Probability & Impact Matrix
o Revised Stakeholder Risk Tolerances
o Reporting Formats and
o Risk Tracking Information
• Based on the guidelines defined in the RM Plan, risks are first identified and added to the risk Register. They are then prioritized during Qualitative risk Analysis and the risk register is further updated with the Risk Ratings which will help us decide which risks to concentrate on and which ones we can worry less about.

Prev: Contents of a RM Plan

Next: Overview of the Risk Register

Wednesday, June 13, 2012

Section Summary - Understanding Risk Management


In this section we have learnt about the basics of Risk Management that will be useful on our journey towards the PMI’s Risk Management Professional Certification.
Let us summarize what have learnt so far:

• A Risk is an uncertain event or condition that if it occurs, has a positive or negative effect on a projects objectives
• Risk Management is the act of increasing the probability and impact of positive events & decreasing the probability and impact of adverse events within a project
• The goal of risk management is to identify the risks within the project and develop a response to either reduce the impact or the probability of a negative risk. If the risk is a positive risk (opportunity) then the goal is to increase the probability and impact of the same.
• The PMBOK Guide covers the Risk Management knowledge area extensively and it is the basis on which our preparation for the RMP Certification is going to proceed
• The Risk Management Plan and the Risk Register are two important documents that are vital to efficient Risk Management
• The Environment in which the Project is executed can have a direct influence on the Project and can be a source of risks for the project. These environmental factors can be grouped into two “Internal” and “External” factors.
• The Project Organizational Structure is one of the vital Internal Factors that affects a Project. An organization can be of 3 types – Functional, Projectized or Matrix. A Matrix Organization in turn can be either a weak matrix, a balanced matrix or a strong matrix
• An Issue is something that is occurring now in the present and is currently being dealt with
• Risk Triggers are signs or indications that is risk event is about to occur or has already occurred. They are also known as Risk Symptoms or Warning Signs
• Pure risk is a type of risk that can result only in losses
• The purpose of Risk Categorization is to systematically identify risks in a consistent manner and organize them so that they can be managed better
• Uncertainty refers to the lack of knowledge of future events whether these events are positive or negative to the project.
• In almost all cases, a risk is taken in pursuit of some kind of benefit
• Part of managing risk is, knowing when to accept a risk.
• The Standard 5 Step approach to managing project risk is widely used to manage project risks and we will use it too. The 5 steps in it are:
o Risk Management Planning
o Information Gathering & Risk Identification
o Risk Assessment & analysis
o Risk Response Planning
o Plan Execution

Prev: Five Step Approach to Risk Management

Next: Risk Management Plan - An Intro

Friday, June 8, 2012

Risk Management & the PMBOK Guide


Are you PMP certified? Or have you read the PMBOK Guide? If so, you would already know that Risk Management is one of the 9 Project Management Knowledge Areas. The Risk Management Knowledge area of the PMBOK Guide will be a valuable resource in your preparation for the Risk Management Professional certification exam. Our exam preparation will closely follow how the PMBOK guide covers Risk Management.

If you are not PMP certified yet or do not have a copy of the PMBOK guide, don’t worry. In my earlier series on the PMP Certification exam preparation, I have covered the area of Risk Management in great detail. If you go through the chapters on Risk Management there, you should have more than enough information to proceed with your RMP exam preparation…

Risk Management Processes – As Per the PMBOK Guide

As per the PMBOK Guide, the Risk Management Knowledge Area is split into 6 distinct processes. Below is a short description of those processes with a link to learn more details about it. Those links contain the details regarding each of these processes from the PMBOK’s Perspective. That will be the basis for us in understanding the details that we will be covering in future from the RMP Exam perspective. So, spend some time and go through those chapters so that you establish the minimum level of knowledge required to easily progress towards the RMP Certification Examination.

The Risk Management Knowledge area includes the following Processes:

1. Plan Risk Management – Risk management planning is the process used to decide how the risk management activities for the project at hand will be performed. You can learn more about this Plan Risk Management process by Clicking Here
2. Identify Risks – The Identify Risk Process is the process where we actually identify all those uncertain events that might affect our project or its outcome. You can learn more about the Identify Risks process by Clicking Here
3. Perform Qualitative Risk Analysis – This is the process where we assess the Probability of the Risk event occurring and the Impact of the same. At the end of this process we will have a prioritized list of risks that we need to analyze further. You can learn more about the Perform Qualitative Risk Analysis process by Clicking Here
4. Perform Quantitative Risk Analysis – This is the process where we take the prioritized list of risks and apply mathematical analysis on them. You can learn more about the Perform Quantitative Risk Analysis process Clicking Here
5. Plan Risk Responses – This is the process where we will be deciding how we are going to handle the risks identified & analyzed in the previous processes if they occur. You can learn more about the Plan Risk Responses process by Clicking Here
6. Monitor & Control Risks – This is the process where we monitor the identified risks and identify & respond to new risks as they appear. You can learn more about the Monitor & Control Risks process by Clicking Here.

The whole Risk Management activity progresses step by step through these 6 processes. This is exactly how this blog is structured too. An important point to note here is that, the output of each of these processes serves as the input to the subsequent process. We will start with Plan Risk Management and progress towards Monitor & Control Risks…


The Risk Management Plan


The Risk Management Plan is the heart of our Risk Management activity and it is the artifact based on which we will be taking up each and every activity of Risk Management. The Risk Management Plan (we will call it RM Plan going forward) is a component of the Project Management Plan. We will be using the following as inputs to create the RM Plan:
a. Cost Management Plan
b. Schedule Management Plan
c. Communications Management Plan
d. Project Scope Statement
e. Organizational Process Assets &
f. Enterprise Environmental Factors

Don’t worry if you think I haven’t given much detail about the RM Plan creation here because there will be a whole section dedicated to it in future…

Key Inputs & Outputs of these Risk Management Processes

The RM Plan is the key output of the Plan Risk Management Process. As outlined in the previous paragraph on the Risk Management processes, the Identify Risks process takes this RM Plan as input and creates the Risk Register as the output. Each of the subsequent processes will take this Risk Register as input and then add or update it with more details and pass it on as input to the next process. This means that the Risk Register is going to be updated multiple times as it goes from Identify Risks to the Monitor & Control Risks process.

Along with the Risk Register, the Monitor & Control Risks process also uses Performance Reports (from the Report Project Performance process) and the Work Performance Information (from the Directing and Managing Project Execution process) that are created during the general Management of the Project. Also, any changes that may be suggested as output of this process will be submitted and put through the Perform Integrated Change Control process.

Prev: What is Project Risk?

Next: Understanding the Project Environment

Sunday, December 18, 2011

Chapter 41: Summary - Project Management Knowledge Areas

Not all project management knowledge areas apply to all projects or project phases. Knowledge areas can interact and overlap.

All the 42 project management processes in the PMBOK are part of one of the nine project management knowledge areas:
1. Integration Management
2. Scope Management
3. Time Management
4. Cost Management
5. Quality Management
6. Human resource Management
7. Communications Management
8. Risk Management
9. Procurement Management

Project Integration Management

The processes that are part of Project Integration Management are:
1. Develop project charter
2. Develop project management plan
3. Direct and manage project execution
4. Monitor and control project work
5. Perform integrate change control
6. Close project or phase

Project Scope Management

The five processes that are part of Project Scope Management are:
1. Collect requirements
2. Define scope
3. Create WBS
4. Verify scope
5. Control scope

Project Time Management

The six processes that are part of Project Time Management are:
1. Define activities
2. Sequence activities
3. Estimate activity resources
4. Estimate activity durations
5. Develop schedule
6. Control schedule

Project Cost Management

The three processes that are part of Project Cost Management are:
1. Estimate costs
2. Determine budget
3. Control costs

Project Quality Management

The three processes that are part of Project Quality Management are
1. Plan quality
2. Perform quality assurance
3. Perform quality control

Project Human Resource Management

The four processes that are part of Project Human Resource Management are
1. Develop human resource plan
2. Acquire project team
3. Develop project team
4. Manage project team

Project Communication Management

The five processes that are part of Project Communication Management are
1. Identify stakeholders
2. Plan communications
3. Distribute information
4. Manage stakeholder expectations
5. Report performance

Project Risk Management

The six processes that are part of Project Risk Management are:
1. Plan risk management
2. Identify risks
3. Perform qualitative risk analysis
4. Perform quantitative risk analysis
5. Plan risk responses
6. Monitor and control risks

Project Procurement Management

The four processes that are part of Project Procurement Management are
1. Plan procurements
2. Conduct procurements
3. Administer procurements
4. Close procurements

Prev: Chapter 40

Next: Chapter 42

Chapter 31: Risk Management during Monitoring & Controlling the Project


Aim: To understand the Monitor and Control Risks process

The monitor and control risk process enables the project manager to keep track of how risk responses are performing against the plan, as well as the place where new risks to the project are managed.

There could be cases in which risk might be identified as having a material impact to the enterprise but not to the project. For these risk types, the project must allow for an alternative communication path that forwards alerts to the people in enterprise risk management functions. In addition, the project manager must remember that risks can have negative and positive effects. For example, consider a project for a bridge that interconnects two roads with a max traffic flow of 10,000 cars and 300 tons. A weather event forces a traffic change from other roads, which doubles the capacity requirements for the bridge for at least 18 months after project completion. Although this wrinkle does not directly affect the project’s deliverable, it is important to consider the new information. In this case, the added traffic could affect the lifespan and performance of the deliverable after delivery.

The table below shows the inputs, tools and techniques, and outputs for the monitor and control risks process.

Monitor and Control Risks
Inputs Tools & Techniques Outputs

Risk register
Project management plan updates
Work performance information
Performance reports

Risk assessment
Risk audits
Variance and trend analysis
Technical performance measurement
Reserve analysis
Status meetings

Risk register updates
Organizational processes assets
Change requests
Project management plan updates
Project document updates
Remember that to determine how much of an effect a risk will have, multiply its probability by its material impact. As the probability of risk materialization increases, the risk register should make resource (money, equipment, people, and time) allocations ahead of time, thus increasing reserves. It is also important that the risk management plan include the processes that would replenish these reserves before they become depleted.

The purpose of project risk control is to
• Identify the events that can have a direct effect in the project deliverables
• Assign qualitative and quantitative weight—the probability and consequences of these events that might impact the project deliverables
• Produce alternate paths of execution for events that are out of your control or cannot be mitigated
• Implement a continuous process for identifying, qualifying, quantifying, and responding to new risks

The risk register accounts for positive and negative risks. A positive risk is a risk taken by the project because its potential benefits outweigh the traditional approach. A negative risk is one that could negatively influence the cost of the project or its schedule.

One of the techniques to evaluate risk control and monitoring effectiveness is to compare actual risk resolution practices to those that were planned at the time the risk was identified. Any deviations (negative or positive), would be cause to implement a corrective action in the risk management plan.

Exam Trivia:
Risk triggers are those events that cause the threat of a risk to become a reality. For example, you have identified the fact that you only have one water pump station available and the replacement takes six weeks to arrive. In the middle of your irrigation and recycling process tests, you discover that water pressure tends to fluctuate beyond pump tolerance levels. If you do not find a way to solve this problem your risk will become a reality.

Remember that for each identified risk, it is important to provide a response plan. It is not much help if the risk becomes a reality and there is no alternate execution path or an emergency procurement plan.

Exam Trivia:
Business risks and pure risks are different because a pure risk takes into account impacts on loss of financial profits, and business risk concentrates on events that might cause a company to lose position with its investors or to have financial difficulty.

In addition, the risk reserves must be evaluated to determine the best way to replenish them. Some examples of events that could have a negative impact in your risk mitigation and control strategies are
• Resource shortage
• Scope creep
• Contractual issues
• Lack of key resources availability

To know more about the Monitor & Control Risks process Click Here

Prev: Chapter 30

Next: Chapter 32

Wednesday, November 2, 2011

Chapter 2: Project Management Knowledge Areas


Aim: To understand the Project Management Knowledge Areas and the Process Groups

The PMBOK organizes all the activities that define a project’s life cycle into 42 processes. These processes are grouped to form nine knowledge areas. It is extremely important to have a good understanding of each of the project processes and how they relate to one another.

We will be taking a detailed look at each of these processes & knowledge areas in the subsequent chapters. Below is the list of 9 Knowledge Areas and the 42 processes.

Knowledge Area Description Processes Covered by the Knowledge Area
Project Integration Management Processes and activities that pull the various elements of project management together, including developing plans, managing project execution, monitoring work and changes, and closing the project. 1. Develop Project Charter
2. Develop Project Management Plan
3. Direct & Manage Project Execution
4. Monitor & Control Project work
5. Perform Integrated Change Control
6. Close Project or Phase
Project Scope Management Processes that ensure the project includes the work required to successfully complete the project, and no more. This includes scope planning, definition, verification, and control. This area also includes the work breakdown structure creation. 1. Collect Requirements
2. Define Scope
3. Create WBS
4. Verify Scope
5. Control Scope
Project Time Management Processes that ensure the project completes in a timely manner. Activity sequencing and scheduling activities occur in this area. 1. Define Activities
2. Sequence Activities
3. Estimate Activity Resources
4. Estimate Activity Durations
5. Develop Schedule
6. Control Schedule
Project Cost Management Processes that ensure the project completes within the approved budget. Basically, any cost management activity goes here. 1. Estimate Cost
2. Determine Budget
3. Control Costs
Project Quality Management Processes that ensure the project will meet its objectives. This area includes quality planning, assurance, and control. 1. Plan Quality
2. Perform Quality Assurance
3. Perform Quality Control
Project Human Resource Management Processes that organize and manage the project team. 1. Develop Human Resource Plan
2. Acquire Project Team
3. Develop Project Team
4. Manage Project Team
Project Communications Management Processes that specify how and when team members communicate and share information with one another and others not on the team. 1. Identify Stakeholders
2. Plan Communications
3. Distribute Information
4. Manage Stakeholder Expectations
5. Report Performance
Project Risk Management Processes that conduct risk management activities for the project. These activities include risk analysis, response planning, monitoring, and control. 1. Plan Risk Management
2. Identify Risks
3. Perform Qualitative Risk Analysis
4. Perform Quantitative Risk Analysis
5. Plan Risk Response
6. Monitor & Control Risks
Project Procurement Management Processes that manage the acquisition of products and services for the project, along with seller and contract management. 1. Plan Procurements
2. Conduct Procurements
3. Administer Procurements
4. Close Procurements
You can learn more about the Project Management Knowledge Areas by Clicking Here

Prev: Chapter 1

Next: Chapter 3

Friday, July 22, 2011

Points to Remember: Project Risk Management

A risk is any uncertain event or condition that might affect your project.

Not all risks are negative. Some events (like finding an easier way to do an activity) or conditions (like lower prices for certain materials) can help your project! When this happens, we call it an opportunity… but it’s still handled just like a risk.

Risk Breakdown Structure (RBS) is a great tool for managing your risk categories. It looks like a WBS, except instead of tasks it shows how the risks break down into categories.

It’s important to come up with probability and impact guidelines to help you figure out how big a risk’s impact is. The impact tells you how much damage the risk will cause to your project. A lot of projects classify impact on a scale from minimal to severe, or from very low to very high. The plan should also give you a scale to help figure out the probability of the risk. Some risks are very likely; others aren’t.

All four of the Risk Management processes are in the Planning process group—you need to plan for your project’s risks before you start executing the project.

The goal of all of the risk planning processes is to produce the risk register. That’s your main weapon against risk. It’s a list of all of the risks and some initial ideas about how you’d respond to them.

The risk register is built into the Risk Management Plan. Updates to the risk register are the only output of the Identify Risks process.

Perform Qualitative Risk Analysis helps you prioritize each risk and figure out its probability and impact. The only output of Perform Qualitative Risk Analysis is the updated risk register.

Sometimes you’ll find that some risks have obviously low probability and impact, so you won’t put them in the main section of your register. Instead, you can add them to a separate section called the watchlist, which is just a list of risks. It’ll include risks you don’t want to forget about, but which you don’t need to track as closely. You’ll check your watchlist from time to time to keep an eye on things.

The first step in risk management is Identify Risks, where you work with the whole team to figure out what risks could affect your project.

Qualitative and quantitative analysis are all about ranking risks based on their probability and impact.

Qualitative analysis is where you take the categories in your risk plan and assign them to each of the risks that you’ve identified.

Quantitative analysis focuses on gathering numbers to help evaluate risks and make the best decisions about how to handle them.

Decision Tree Analysis is one kind of Expected Monetary Value analysis. It focuses on adding up all of the costs of a decisions being made on a project so that you can see the overall value of risk responses.

To calculate EMV, be sure to treat all negative risks as negative numbers and all opportunities as positive ones. Then add up all of the numbers on your decision tree.

Don’t forget watchlists. They let you monitor lower-priority risks so that you can see if triggers for those risks occur and you need to treat them as higher priorities.

All of the processes in Risk Management are Planning or Monitoring & Controlling processes. There are no Executing processes here. Since the goal is to plan for risks, there is no need to focus on actually doing the work. By then, it’s too late to plan for risks.

Your risk register should include both threats and opportunities. Opportunities have positive impact values, while threats have negative ones. Don’t forget the plus or minus sign when you’re calculating EMV.

Plan Risk Responses is figuring out what you’ll do if risks happen.

Risk monitoring should be done at every status meeting.

The better you prepare for risks, the more secure your project is against the unknown.


Points to Remember - Other Topics:

Introduction to Projects & Project Management
Relationship Between Knowledge Areas & Process Groups
Project Integration Management
Project Scope Management
Project Time Management
Project Cost Management
Project Quality Management
Human Resource Management
Project Communication Management
Project Procurement Management
Ethics & Professional Responsibility

Thursday, June 30, 2011

Chapter 51: Identifying Risks

In the previous chapter, we learnt that managing risks is a big and important task. But, in order to manage and mitigate risks, the first thing we need to do is to identify them. In this chapter, we are going to learn just that.

So, lets get started!!!

Identifying Risks

Risks are identified by using the risk identification process. An unidentified risk is a danger lurking out of your sight and waiting to attack the project. The significance of the risk identification process cannot be explained enough. Organizations have whole departments whose sole purpose is to identify and mitigate risks. I guess, this is enough to quantify how important risk management is to large organizations. Similarly, from the perspective of running a project as a project manager too, risk management is extremely important and to do that effectively, first you need to identify those risks.

You use the risk identification process to accomplish the following tasks:
• Identify which risks might affect the project at hand
• Document the characteristics of the identified risks in a document called the risk register

As with all process, the risk identification process too has a set of inputs, uses some tools & techniques and produces an output. It is explained in the picture below:


Input to Risk Identification

The risk management plan and the project scope baseline are obvious inputs to identifying risks. As in many other processes, the enterprise environmental factors and organizational process assets relevant to the project at hand must also be considered. The following are all the inputs that need to be considered in the risk identification process.

Project scope baseline - Assumptions in the project scope statement, an element of the scope baseline, are potential sources of uncertainty, hence the risk. Constraints pose a risk by presenting predetermined factors, such as hard deadlines and fixed costs, thereby posing questions such as, “What is the probability that we can meet this constraint with the available resources?”

The WBS, another component of the scope baseline, can be used to recognize risks at different levels of the WBS hierarchy.

Management plans - In the process of identifying risks, you need to look at the cost management plan, schedule management plan, risk management plan, and quality management plan. The approach that any of these plans takes may pose some risks of its own or may enhance some other risks. The key items from the risk management plan useful for risk identification are risk categories, roles and responsibilities, and the budget and timing available for the risk management activities.

Cost and duration estimates - Estimates such as activity cost estimates and activity duration estimates by definition have a degree of uncertainty built into them. They should be looked at carefully to identify the potential risks hiding behind this uncertainty.
Stakeholder register - If you look at the stakeholder register, you might find some stakeholders who can give useful input to identifying risks.

Enterprise environmental factors - The environmental factors internal or external to the performing organization that can influence the project must be considered in the risk identification process. This might include academic and industry studies, published information, benchmarking, and commercial databases.

Organizational process assets - This might include information from previous projects including lessons learned, process controls, and risk-related templates.

Tools and Techniques for Risk Identification

Risk identification is crucial to risk management. If you fail to identify a risk, you will not be able to manage it. Having all these inputs is fine, but the key to the whole process is to identify the risks properly. The tools and techniques we use in this process are:

Assumptions analysis - Assumptions in the project scope statement represent uncertainty. You analyze these assumptions to identify the risks. Assumptions analysis is the technique used to examine the validity of the assumptions and thereby to identify the risks resulting from the inaccuracies, inconsistencies, or incompleteness of each assumption. For example, suppose there is only one person in the organization who has a rare skill needed for the project. An obvious assumption would be that the person will not quit the organization before completing the Project. Ignoring this fact constitutes a potential risk.

Checklist analysis - The carefully prepared checklists in any process are great no-brainer timesavers. Projects in the same organization will more often than not have similarities. As a result, you can develop a risk identification checklist based on the information gathered from a similar set of projects previously performed. Also, if you developed the risk breakdown structure (RBS) in risk planning, the lowest level of the RBS can be used as a checklist.

Diagramming techniques - These techniques use diagrams to identify risks by exposing and exploring the risks’ causes. Here are a few examples:
• Cause-and-effect diagram - A cause-and-effect diagram illustrates how various factors (causes) can be linked to potential problems (effects).
• Flowchart diagram - A flowchart depicts how the elements of a system are related to each other and shows the logical flow of a process. By examining the flowchart of a process, the risk management team can identify points of potential problems in the flowchart diagram.
• Influence diagram - An influence diagram is a graphical representation of situations that shows relationships among various variables and outcomes, such as causal influences and time-ordering of events. By examining these diagrams, the risk management team can recognize potential problem areas and thereby identify risks.

Documentation reviews - A structured review of the relevant parts of input documents, such as the project scope statement and the project management plan, will definitely help in identifying risks. Furthermore, the knowledge base related to risk management from previous projects can also be used/reviewed.

Information-gathering techniques - To identify risks, you need to gather risk related information. Following are some of the information gathering techniques used in risk identification:
• Brainstorming - The goal here is to get a comprehensive list of potential risks so that no risk goes unidentified. The project team, along with relevant experts from different disciplines, can participate in the brainstorming session. Brainstorming is better performed under the guidance of a facilitator or a moderator. You can use the categories of risks or the RBS as a framework to keep the session focused on the issue.
• Delphi technique - The goal here is for experts to reach a consensus without biases toward each other. I’m sure you will have no problem recalling a time when a decision was made because somebody (usually higher in the management hierarchy) said so. Contrary to this, the Delphi technique is used to ensure that it is the quality of the information and the argument that are important, not who is saying them. It is more or less like a democracy wherein a person putting forth an argument has to convince everyone rather than expect them to nod their heads because he/she is the boss. A facilitator circulates a questionnaire among the experts to solicit ideas about the risks of the given project. The experts respond anonymously. The responses are compiled and circulated among the participating experts for further evaluation without attaching a name to a response. It might take a few iterations before a general consensus is reached.
• Interviewing - This is one of the common methods used for information gathering for risk identification. You interview the appropriate stakeholders and subject-matter experts to gather information that will help identify risks for the project at hand.
• Root cause identification - A powerful way to identify risk is to look for anything in the project that might generate a risk. In other words, if you can spot a potential cause for risks, it’s simple to identify the risks resulting from that cause. Furthermore, if you know the cause of a risk, it helps to plan an effective response. You can also look for risks at the opposite side of causes that is, impacts.
• SWOT analysis - While root cause identification techniques look into the causes of risks to identify risks, a SWOT analysis looks at the potential impacts of risks to identify risks. If you examine the strengths, weaknesses, opportunities, and threats (SWOT) of a given project, you will be exposing the risks involved. Remember that a strength is an opportunity, a weakness is a threat, and opportunities and threats are posed by risks. This helps broaden the spectrum of risks considered. For example, a strength of your project might be that most of its parts are well understood from previously executed similar projects. Therefore, the risks involved in those parts will be easy to identify. A weakness of your project might be that one of the parts involves new technology that is not well-tested. So, this is a source of unknown risks. An opportunity might be that your organization will be the first one to take this product to market. An example of a threat might be that the government is considering a bill that, if it becomes a law, will have profound implications for your project.

Of course, you can always use the judgment of experts on the topic. You will generally be using more than one of these tools and techniques to identify risks. During risk identification, you might discover the causes of the risks, and you might even think of some potential risk responses. All this is part of the output of the risk identification process.

The Output of Risk Identification - The Risk Register

The risk register is a document that contains the output of the risk identification process. The risk register will be constantly updated with a lot of information from other risk management processes. To begin, you store the following information from the risk identification process in the risk register:
• List of identified risks - These are the risks that you identified in the risk identification process. These risks should be described in reasonable detail, which may include the following:
o The risks - The definition and nature of each risk and the causes that will give rise to the risk.
o List of the root causes of the risks - This is a list of events or conditions that might give rise to the identified risks.
o Updates to risk categories - Risks categories were originally identified in the risk management planning process. However, in the process of identifying risks, you might discover new categories or modify existing categories. The updated risk categories must be included in the risk register.
• List of potential responses - Risk response planning is a separate process that is performed after risk analysis. However, during risk identification, you might identify potential risk responses that you must document in the risk register. These responses can be further examined and planned in the risk response planning process.

The results of the risk identification process usually lead to qualitative risk analysis. However, depending upon the project and the experience of the risk management team, risk identification might lead directly to quantitative risk analysis and even to risk response planning.

Prev: Planning Risk Management

Next: Analyzing Risks

Wednesday, June 29, 2011

Chapter 50: Planning Risk Management

In the previous chapter, we saw the big picture of risk management and the next step now is to plan for managing risks in our project.
So, lets get started!!!

Planning Risk Management

Risk management planning is the process used to decide how the risk management activities for the project at hand will be performed. The major goals for planning risk management are threefold: Ensure that the type, level, and visibility of risk management are proportionate to the actual risk involved in the project and the importance of the project to the organization; secure sufficient resources, including time for risk management activities; and set up an agreed-upon basis for evaluating risks.
To be more explicit, you use the risk management planning process to determine the following:
• How to approach the risk management activities for this project
• How to plan the risk management activities
• How to execute the risk management activities
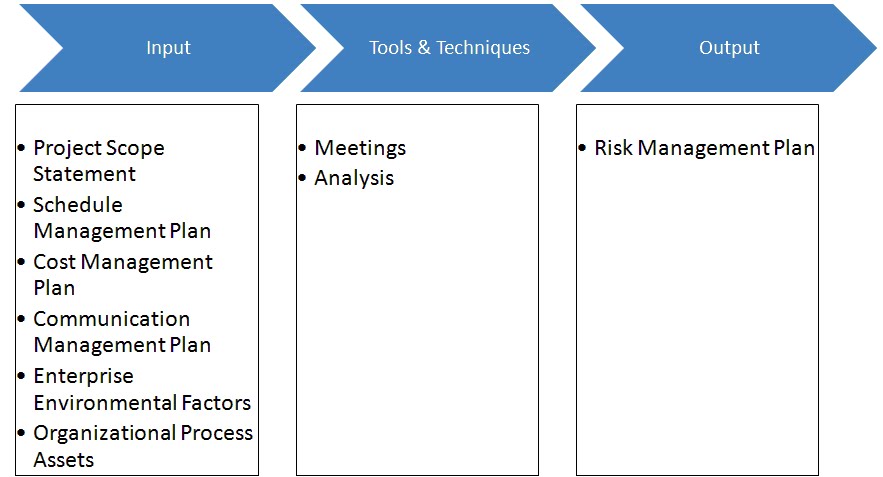
The picture below explains the process used for Planning Risk Management:


Developing the Risk Management Plan

You perform risk management planning to develop a document called the risk management plan. As an input to this development process, you need to look at the project scope statement, which contains elements such as the following, which are relevant to risk management planning:
• Assumptions and constraints - Assumptions should be evaluated for their uncertainty and thereby the possible risks. Constraints represent fixed parameters, such as available funds and deadlines that can also pose risks to the project.
• Project objectives and requirements - You must address the risks that might prevent the team from meeting the project objectives and requirements.
• Product description - There might be risks involved in performing the work for meeting the product description.
• Initial risk identification - The project scope statement might contain some of the risks you initially identified. Now you have more information to build on that work.
The cost management plan may have information on risks related to budget, contingency, and management reserves. The schedule management plan may have information on how the schedule contingencies will be used and reported. The communication management plan should have information on who should receive reports about the different risks.

The enterprise environmental factors relevant to risk planning include the organizational attitude toward risks and the risk tolerance level of the organization. This information can be found from the policy statements of the organization and from actual experience with previous projects. The organizational process assets relevant to risk planning include organizational approaches toward risk management, definitions of concepts and terms used within the organization, standard risk templates you can use, a roles and responsibilities list, and authority levels for decision making.

You develop the risk management plan by holding planning meetings, which might include the following attendees:
• Project manager
• Selected members from the project team (Usually the team leads and other experienced members of the team)
• Selected stakeholders
• Any member from the performing organization who has responsibility for risk planning and executing

In these meetings, the input items are used to develop the risk management plan, the only output of the risk management planning process.

Risk Management Plan

The only output of the Plan Risk Management process is the risk management plan, which includes the following elements.

Methodology - This specifies the system of approaches, tools, and data sources that will be used to perform risk management on the project at hand. These tools and approaches might vary over projects, so you have to make the best selection for the given project.
Identifying and assigning resources - This identifies and assigns resources for risk management, such as human resources, cost, and time.
• Roles and responsibilities - This specifies the roles and responsibilities for each role involved in risk management. These roles are assigned to members of the risk management team. The risk management team might include members from outside the project team.
• Budgeting - The cost for risk management activities needs to be estimated and included in the budget and the project cost baseline.
• Timing and scheduling - The plan specifies how often risk management processes will be performed and which risk management activities will be included in the project schedule, which is planned and developed by using processes discussed in the chapter on Planning for Project Schedule and Communication.

Risk categories - This element specifies how the risks will be categorized. The risk categories typically correspond to the sources of risks. Depending upon the size and complexity of the project, you might need to develop a risk breakdown structure (RBS), which is a hierarchical structure that breaks the identified risk categories into subcategories. In developing this structure, you will end up identifying various areas and causes of potential risks. The performing organization might already have prepared a categorization of typical risks. However, you need to examine this categorization for each project and tailor it according to the needs of the project at hand. The risk categorization helps you identify risks to the extent that you will be identifying various areas and causes of potential risks for your project.

Risk probability and impact - Defining different levels of risk probabilities and impacts is necessary to ensure the quality and credibility of the qualitative risk analysis that we will discuss in just a bit. The basic issues are defining the scale of likelihood that the risk will happen and defining the scale of the strength of its impact if the risk occurs. These definitions, even if they already exist in the organization, must be examined and tailored to the needs of the specific project.

You can define the risk probability scale from very unlikely to almost certainly, called the relative scale. As an alternative, you can define a numerical scale in which the probability is represented by numbers, in which a value close to 0.0 means very unlikely and a value close to 1.0 means almost certainly. The impact scale represents the size of the risk impact on the given project objective should the risk occur. Just like the probability scale, you can define the impact scale relatively or numerically. The relative scale can range from very low impact to very high impact, with points in the middle such as low, moderate, and high. As an alternative, you can define the impact numerically; it might be linear, such as the first point at 0.1, the second point at 0.2, and the tenth point at 1.0, or it might be nonlinear, such as the first point at 0.001, the second point at 0.01, and the third point at 0.1.

Look at the picture below for a simple example: It shows an example of linear and nonlinear impact scales, in which the impact scale for Objective 1 is nonlinear and the impact scale for Objective 2 is linear. You can think of the X axis as a variable on which the risk impact depends.


Risks are prioritized according to the size of their impact on the project objectives, which can be recorded in what is called an impact matrix or lookup table. Even if your organization already has a typical impact matrix, you should examine it and tailor it to the needs of the specific project at hand. I will discuss the probability and impact matrix in more detail later in this chapter.

To understand the risk impact better, lets look at a sample that defines the impact of risks on the various project objectives.

Project Objectives Very Low (0.05) Low (0.10) Moderate (0.35) High (0.65) Very High (0.90)
Time Insignificant time increase 1-10% time increase 10-30% time increase 30-60% time increase 60-100% time increase
Cost Less than 1% cost increase 1-20% cost increase 20-50% cost increase 50-80% cost increase 80-100% cost increase
Scope Scope decrease unnoticeable Scope of only a few minor areas affected Sponsor approval necessary for scope reduction Scope reduction unacceptable to the sponsor Project and item are effectively useless
Quality Unnoticeable quality reduction Only a few applications will be affected Quality requires sponsor approval Quality reduction unacceptable Project and item are effectively useless
A point to note is that, this example shows only the negative impact.

Risk reporting and tracking - This element describes the format of risk reports, such as the risk register, a document that contains the results of risk analysis and risk response planning. Furthermore, it describes how different aspects of risk activities will be recorded so that the risks can be monitored for the current project. Also, should the performing organization decide to audit the risk management process, one should be able to track these activities. Another reason for recording these activities could be to save the information for the benefit of future projects in the form of lessons learned.

During the process of planning risk management for a specific project, you revisit the tolerance levels of the stakeholders for certain risks, and these levels may be revised. Risk management planning is the process that generates the risk management plan document, which contains the information that will be used in risk identification, risk analysis, and risk response planning.
You cannot manage a risk if it’s not identified. Dont worry, thats going to be the next chapter.


Prev: Big Picture of Risk Management

Next: Identifying Risks

Thursday, June 23, 2011

Chapter 49: The Big Picture of Risk Management

The word Risk signifies or means Danger and our perception is that, whenever it happens, the result will be negative or something undesirable. That’s the general description but we are preparing for PMP and what the PMI says matters!!!

According to PMI

Risk is an uncertain event or condition that if occurs, has a positive or negative effect on meeting the project objectives related to components such as schedule (time), cost, scope or Quality.

For example, one of the obvious schedule objectives for a project is to complete the project by the scheduled deadline. If a risk related to the schedule occurs, it can delay the completion of the project, or it can make it possible to finish the project earlier. So, the two characteristics of a risk in project management are the following:

• It stems from elements of uncertainty.
• It might have negative or positive effects on meeting the project objectives.

Risk management includes planning risk management, identifying and analyzing the risks, preparing the response plan, monitoring the risk, and implementing the risk response if the risk occurs.

Look at the picture below that explains the big picture of Risk Management


The picture above shows the corresponding processes used to accomplish these tasks, which are also explained below:
• Plan Risk Management - A process to determine the how of risk management: how to conduct risk management for the project at hand.
• Identify Risks - A process to identify and document the risks that might occur for a given project.
• Perform Qualitative Risk Analysis - A process used to estimate the overall probability for risks to occur and their impact and to prioritize them accordingly for further analysis.
• Perform Quantitative Risk Analysis - A process used to analyze numerically the effect of identified risks on meeting the project objectives.
• Plan Risk Responses - A process used to prepare a risk response plan in order to increase the positive impact and decrease the negative impact of risks on the project.
• Monitor and Control Risks - A process used for tracking identified risks, identifying new risks, executing risk response plans, and evaluating the effectiveness of executing responses throughout the lifecycle of the project.

The risk monitoring and control process is part of the control process group; therefore, we will discuss them later while discussing Monitoring and Controlling Quality and Risk. The other five processes will be discussed in the next few chapters.

Trivia:
The data flow between the different processes as shown in the picture above is true in general. However, a point to note is that, depending upon the project and the experience of the risk management team, shortcuts can be taken. For example, you can go directly from risk identification to quantitative risk analysis, or even to risk response planning depending on how comfortable you are with respect to these tasks.

Prev: Planning Quality

Next: Planning Risk Management

Chapter 46: Introduction to Quality & Risk Management

Till now we have covered how to plan for a project scope, project resources and project procurement. The next planning we need to do is “Planning the Projects Quality & Risk”. In the next few chapters, we will be covering these in details.

So, lets get started!!!

Why Quality & Risk Management is Essential?

Quality and risk are two important interrelated aspects of any project that need to be managed. While quality refers to the degree to which a set of characteristics of project deliverables and objectives fulfill the project requirements, risk refers to an uncertain event or condition that, if it occurs, has a positive or negative effect on meeting the project objectives.

Consider the following two scenarios:

Scenario 1:

Your project just went live. You have created an online banking website for some bank in America and the website is live. As soon as customers start using the website, it is frequently crashing, customers are not able to view their account balance or perform fund transfer. All in all, the website isn’t meeting its required objectives. What went wrong here?

There was no quality management done. The quality of the work product delivered to the customer isn’t up to expectations and hence it’s a total disaster.

Scenario 2:

Lets say, you are on your way to deliver a major online banking website for a large bank in America. You are midway through the project and suddenly your Technical Lead has resigned. He was the center point for all technical discussions in the project and his departure is going to leave a big void and now people are worried that we may not be able to finish the project. What went wrong here?

There was no risk management done. Every project has its own set of inherent risks that may delay the project delivery and if we fail to plan for such risks, the project will be a total disaster.

After you have planned the project scope to the WBS level, as discussed in the previous chapters, you are ready to plan the quality and risk management. After the project starts executing, you will not have enough time to plan a response to a risk if it occurs, so you need to plan risk responses before the project starts executing. To do that, you need to identify the risks and analyze them.

So, the main things we will learn in this section are:
1. How do you plan for quality and risk management?
2. Learn how to plan quality
3. Identify and analyze risks
4. Plan risk responses.

This chapter is just an introduction and we will jump into the details in the subsequent chapters.

Prev: Important Terms - Project Resource Planning

Next: Big Picture of Quality Management
© 2013 by www.getpmpcertified.blogspot.com. All rights reserved. No part of this blog or its contents may be reproduced or transmitted in any form or by any means, electronic, mechanical, photocopying, recording, or otherwise, without prior written permission of the Author.

Followers

Popular Posts